I cloned my voice with free AI tools - and tested a scam call on my family - ZDNET
Your social media posts could give scammers all the audio they need. Would your loved ones spot the fake?
Your social media posts could give scammers all the audio they need. Would your loved ones spot the fake?

Researchers linked alleged iPhone crypto theft via websites to DeadTag, finding spyware code on 6,600 legitimate sites that could expose older devices. The post Researchers Trace Alleged DeadTag iPhone Spyware to 6,600 Websites appeared first on Bitcoin Found…
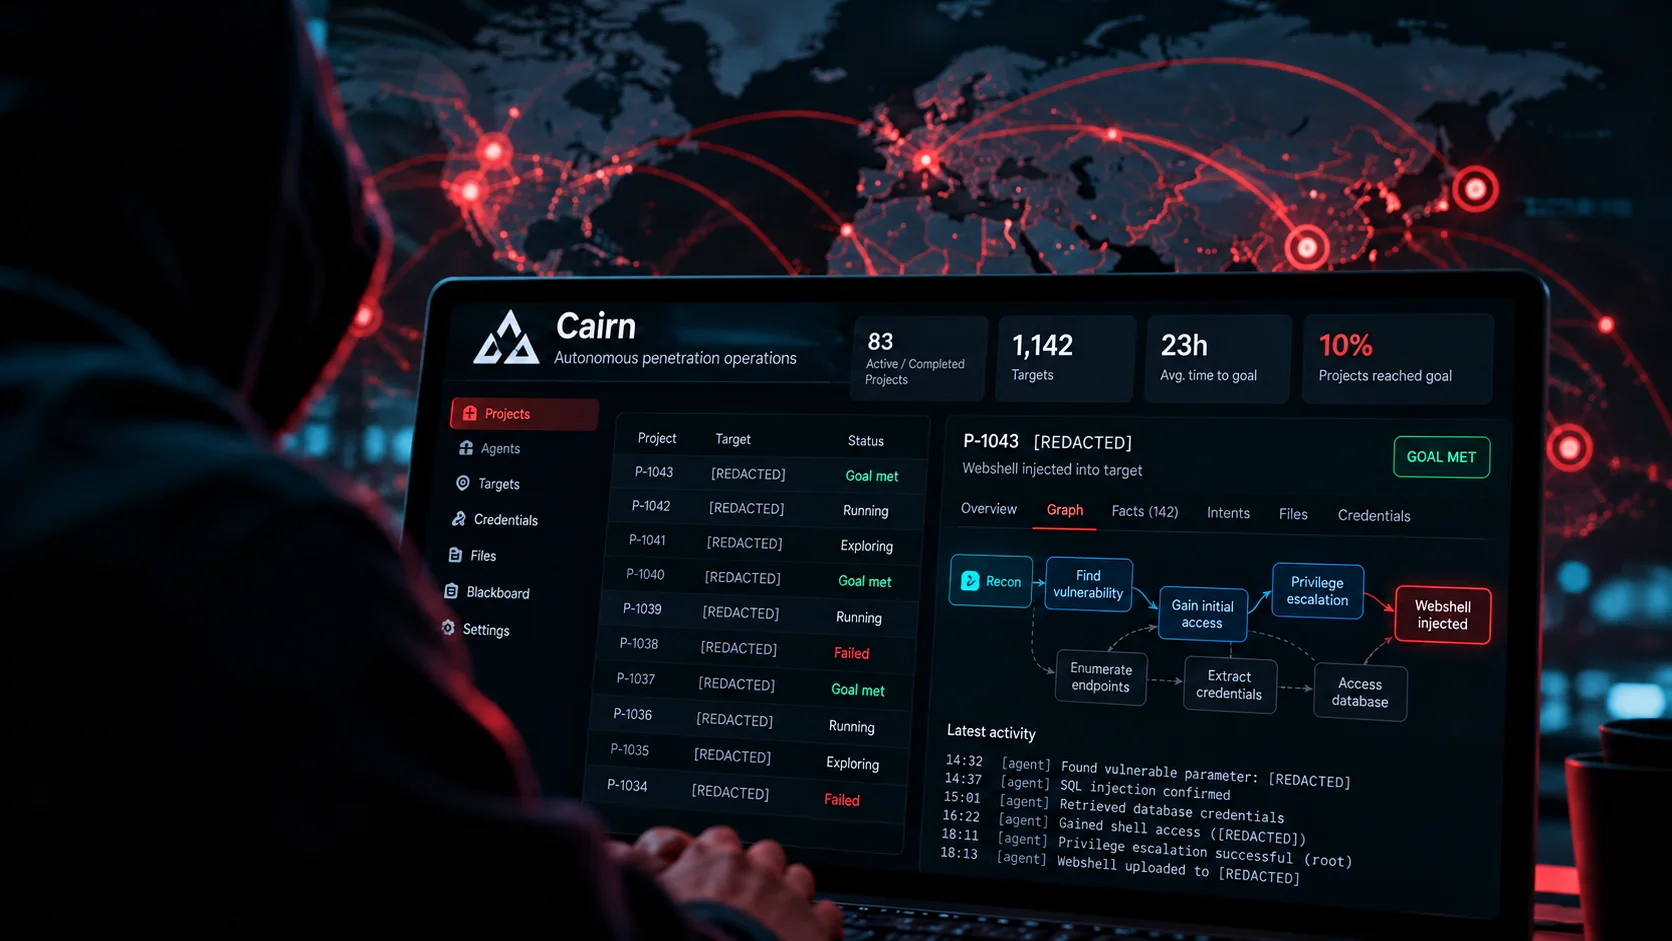
https://www.reuters.com/legal/government/how-one-hacker-used...https://www.theverge.com/ai-artificial-intelligence/1013643/... Comments URL: https://news.ycombinator.com/item?id=50152302 Points: 8 # Comments: 2
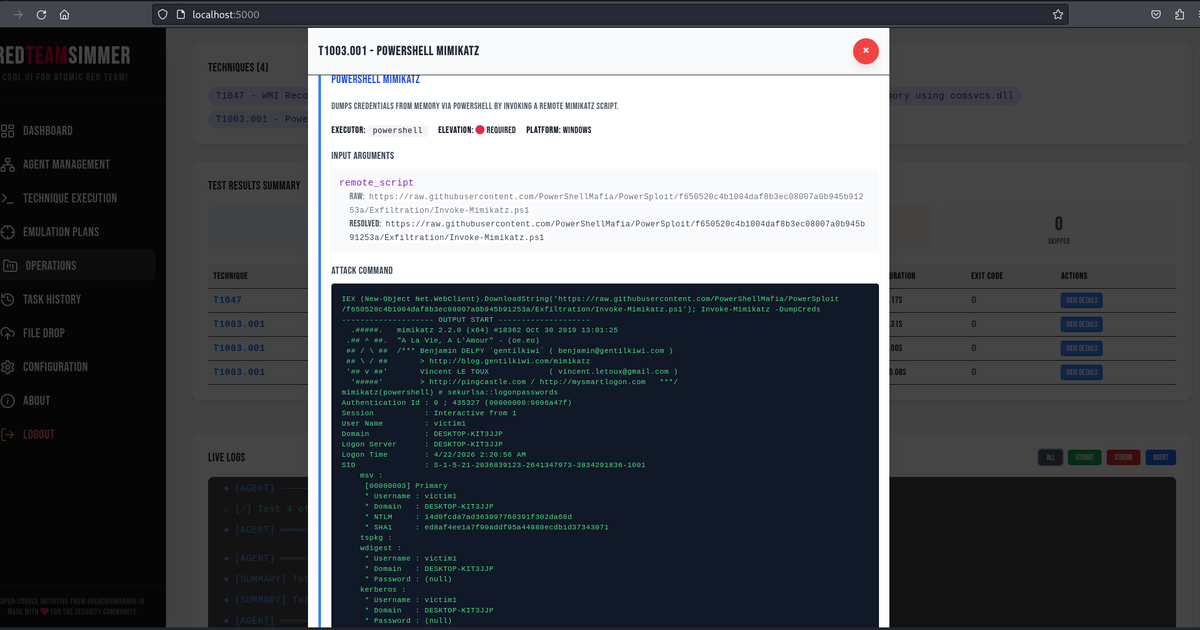
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT emulation plans, and detection rule correlation.
A quarter of victims of deepfake attacks have lost over $1m. CISOs worry that boardrooms don’t understand the threat
Sekoia and Kudelski Security have observed that North Korea's Lazarus umbrella is split into six distinct clusters, focused on espionage, financial theft and sanctions evasion
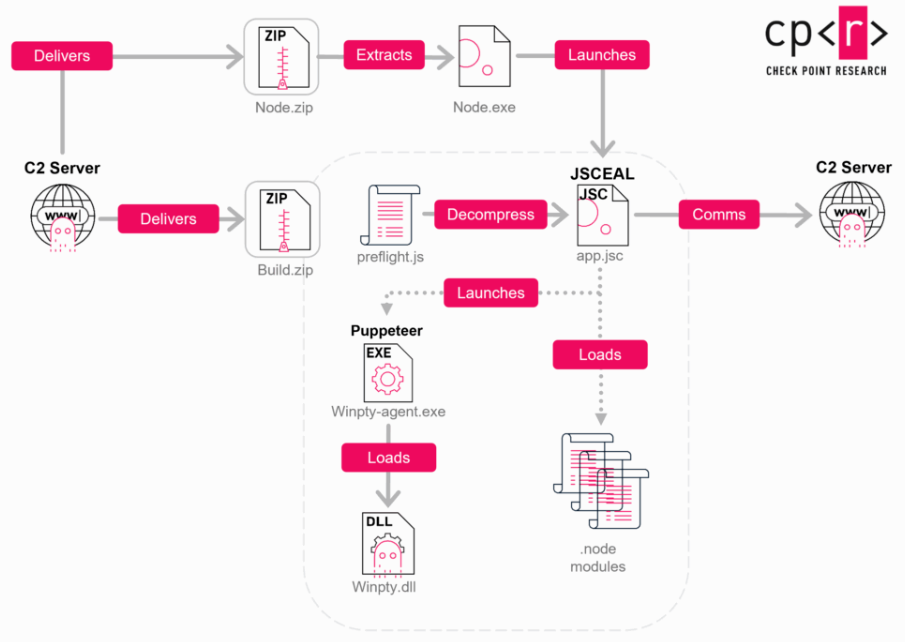
JSCeal hides crypto-stealing malware in V8 bytecode, but researchers built a tool to decompile it and expose its advanced theft capabilities. JSCeal is a cryptocurrency stealer that Check Point Research has tracked since early 2025. Unlike most malware, it hi…
Yowza...this is pretty wild! The post He’s Taking His Condo Board to Court Over a Long List of Issues — One of Them a Felony appeared first on TwistedSifter.

Claude users are being signed out of their accounts to stop a new malware campaign that is draining their AI usage.

Cybersecurity researchers have identified a set of 13 malicious Composer theme packages on Packagist that are designed to inject JavaScript into Vietnamese movie and comic streaming sites that install those libraries and initiate the deployment of spyware aim…
ToxicPanda sounds like an energy drink formulated for people who regard sleep as a character flaw. It’s actually an Android banking Trojan capable of taking over phones, stealing financial credentials and initiating unauthorized transactions. Its newly discov…

You said: trump engineer chaos stock markets chossudovsky 2:55 p.m . Michel Chossudovsky has argued that the global financial system is facing outright criminalization and financial theft on an unprecedented scale, a p…
ZeroTokens gives phishing operators live control of victim sessions targeting 53 financial brands

T-Mobile's proactive security measures highlight the critical need for robust defenses in telecom, influencing industry-wide security standards. The post T-Mobile cuts cable to expel Chinese hackers from network appeared first on Crypto Briefing.
A new Android NFC relay malware called WindRelay is being used alongside the SpyNote remote administration tool (RAT) to steal live card data and send it to attackers in real time. [...]
A 26-year-old California man allegedly stole over $97,000 from an 89-year-old retiree by resetting his Coinbase password after meeting at a breakfast club; he faces elder abuse and theft charges following a multi-agency probe. The post California Man Accused …

An 89-year-old retiree was swindled out of more than than $97,000 in a crypto theft scheme, cops said. William Ly, 26, of Simi Valley was arrested Aug. 4 on suspicion of financial elder abuse, grand theft and identity theft following a months-long investigati…

A former Oak Run Elementary School District Superintendent, who was fired "without cause" in 2025, is suing both the School District and the Shasta County Office of Education.
The cybersecurity firm, Genians, said it found evidence that the North Korean-linked group Kimsuky had set up tools for running and managing AI models locally, including Ollama, GPT4All and Msty, alongside document search technology known as retrieval au…

Fake "coordinated hardware audit" emails are steering holders to a cloned Coldcard site that installs remote-access software.
Russian hacking group Star Blizzard targeted US nuclear scientists after refining phishing tactics on Ukrainian victims, raising cybersecurity The post Russian hackers target US nuclear scientists after testing cyber tactics in Ukraine appeared first on Crypt…